01
Nothing risky runs unwatched
Every action outside your approved scope pauses and waits for a one-tap sign-off. Kaer never escalates its own permissions.
Human-in-the-loop
Kaer runs your runbooks end-to-end — health checks, migrations, deploys — and pauses the moment any action needs sign-off. Nothing risky executes without a human in the loop.
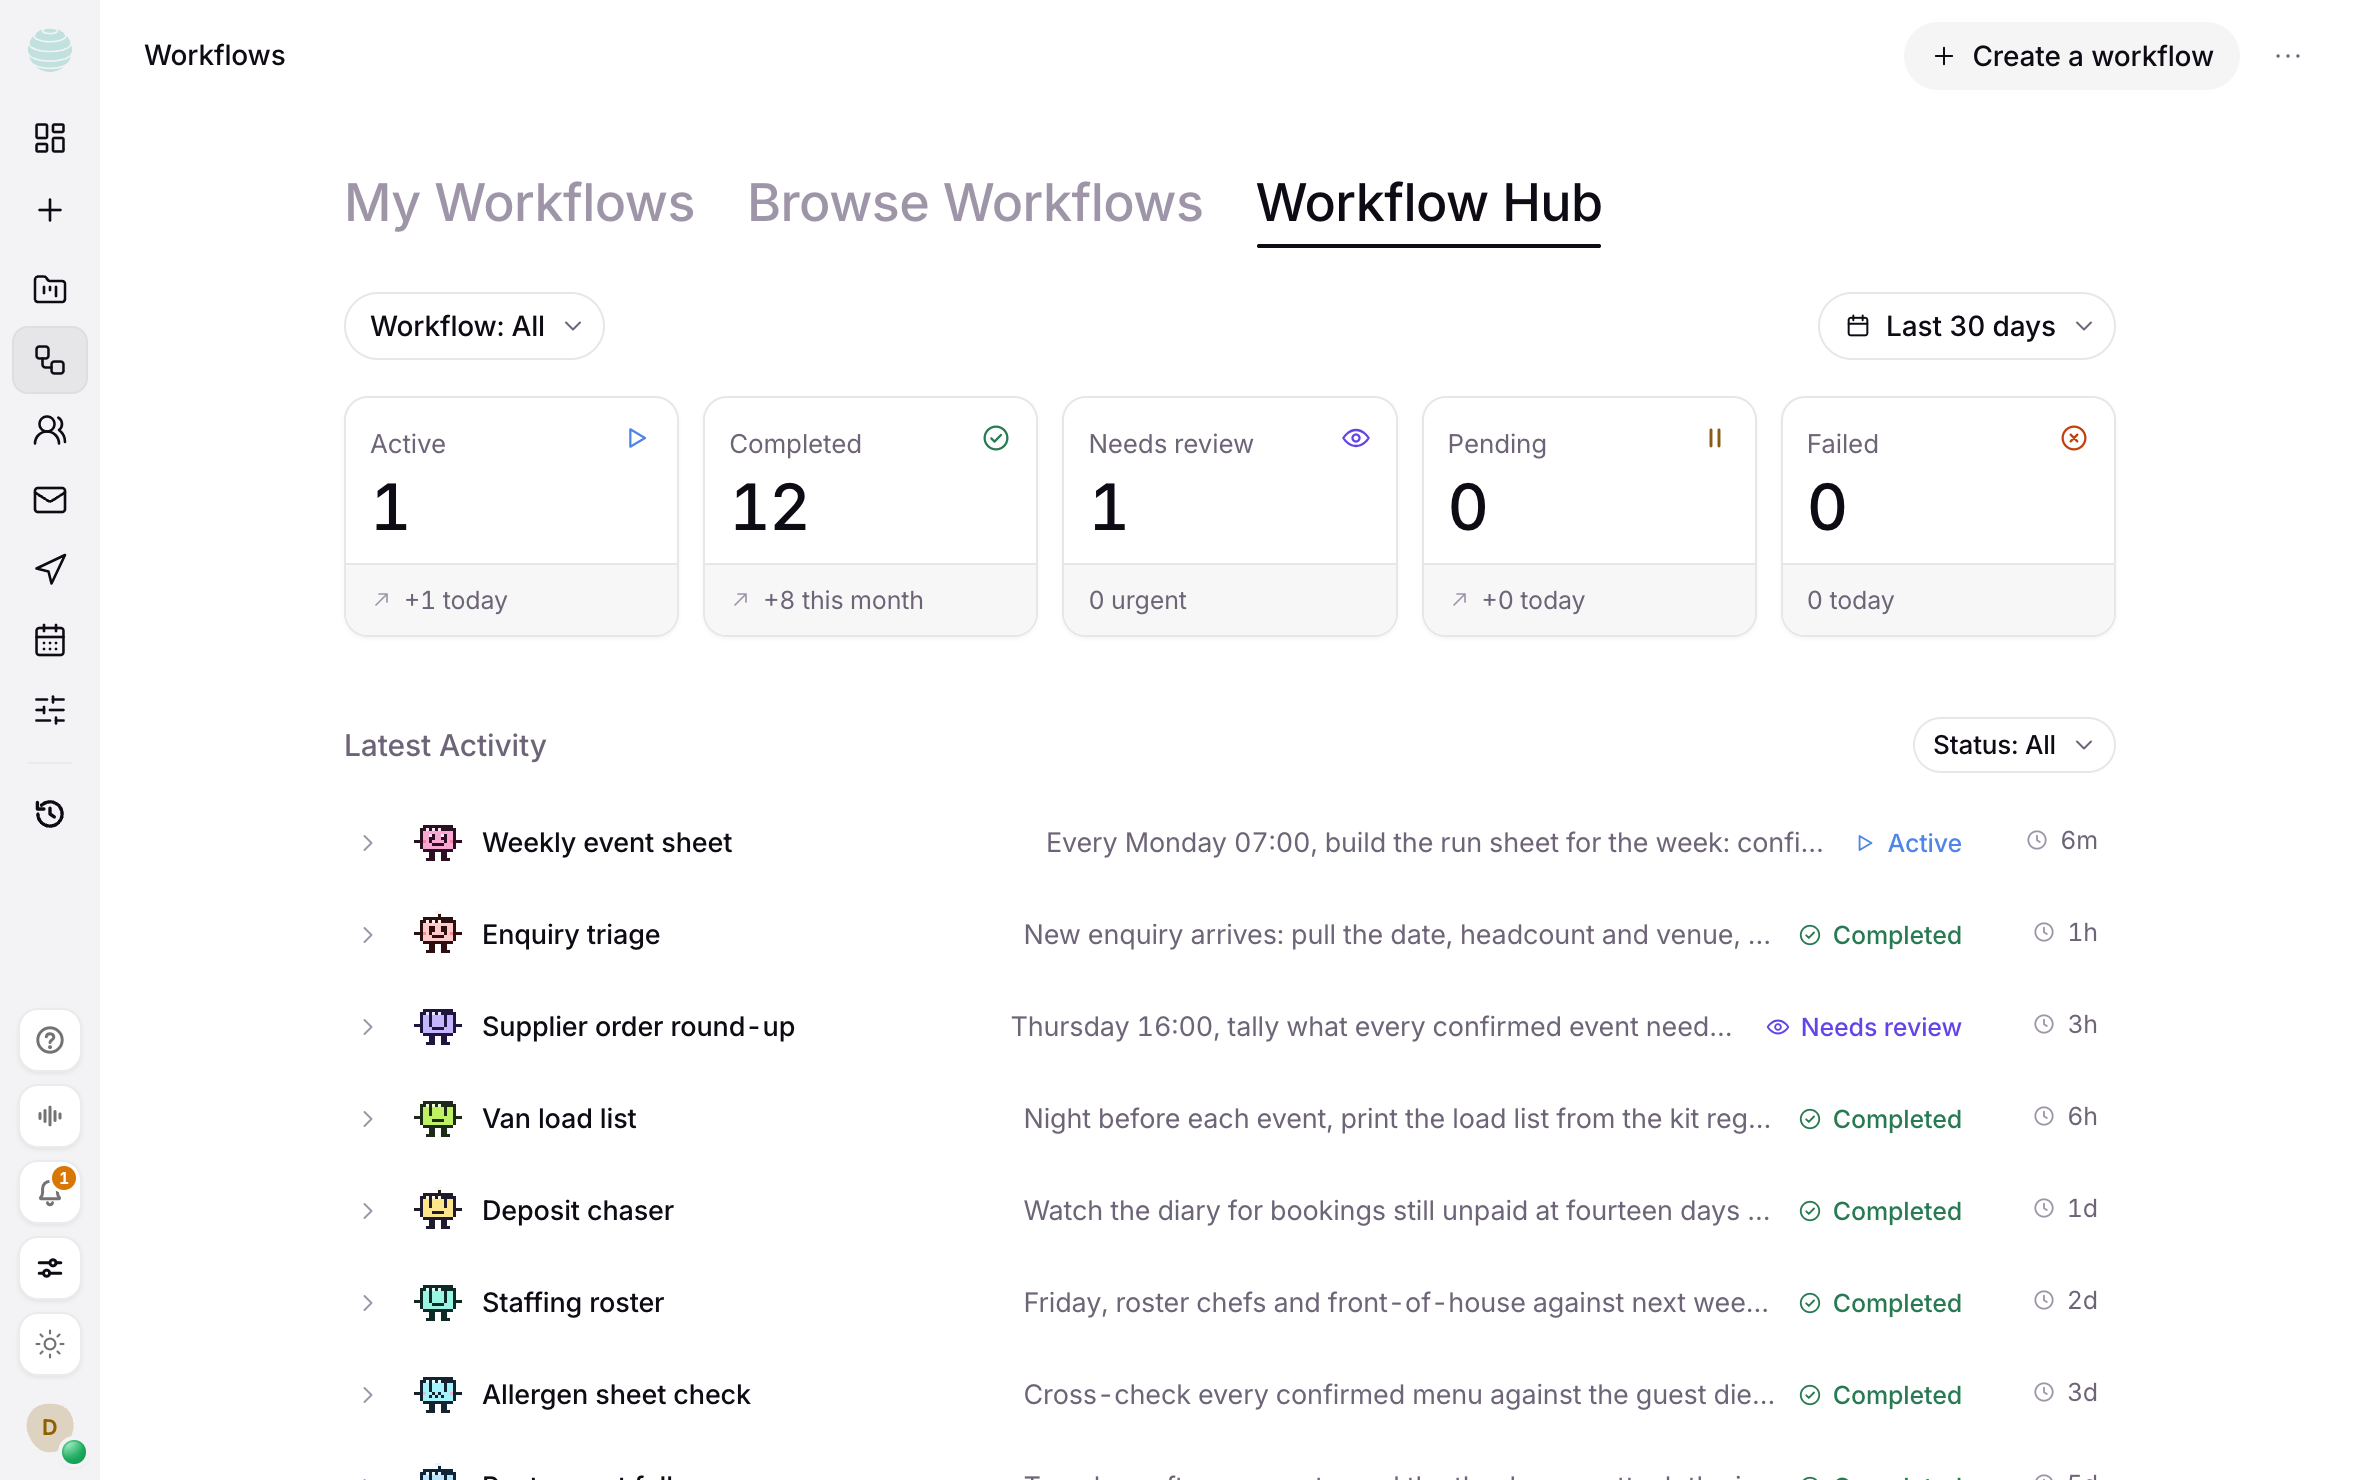
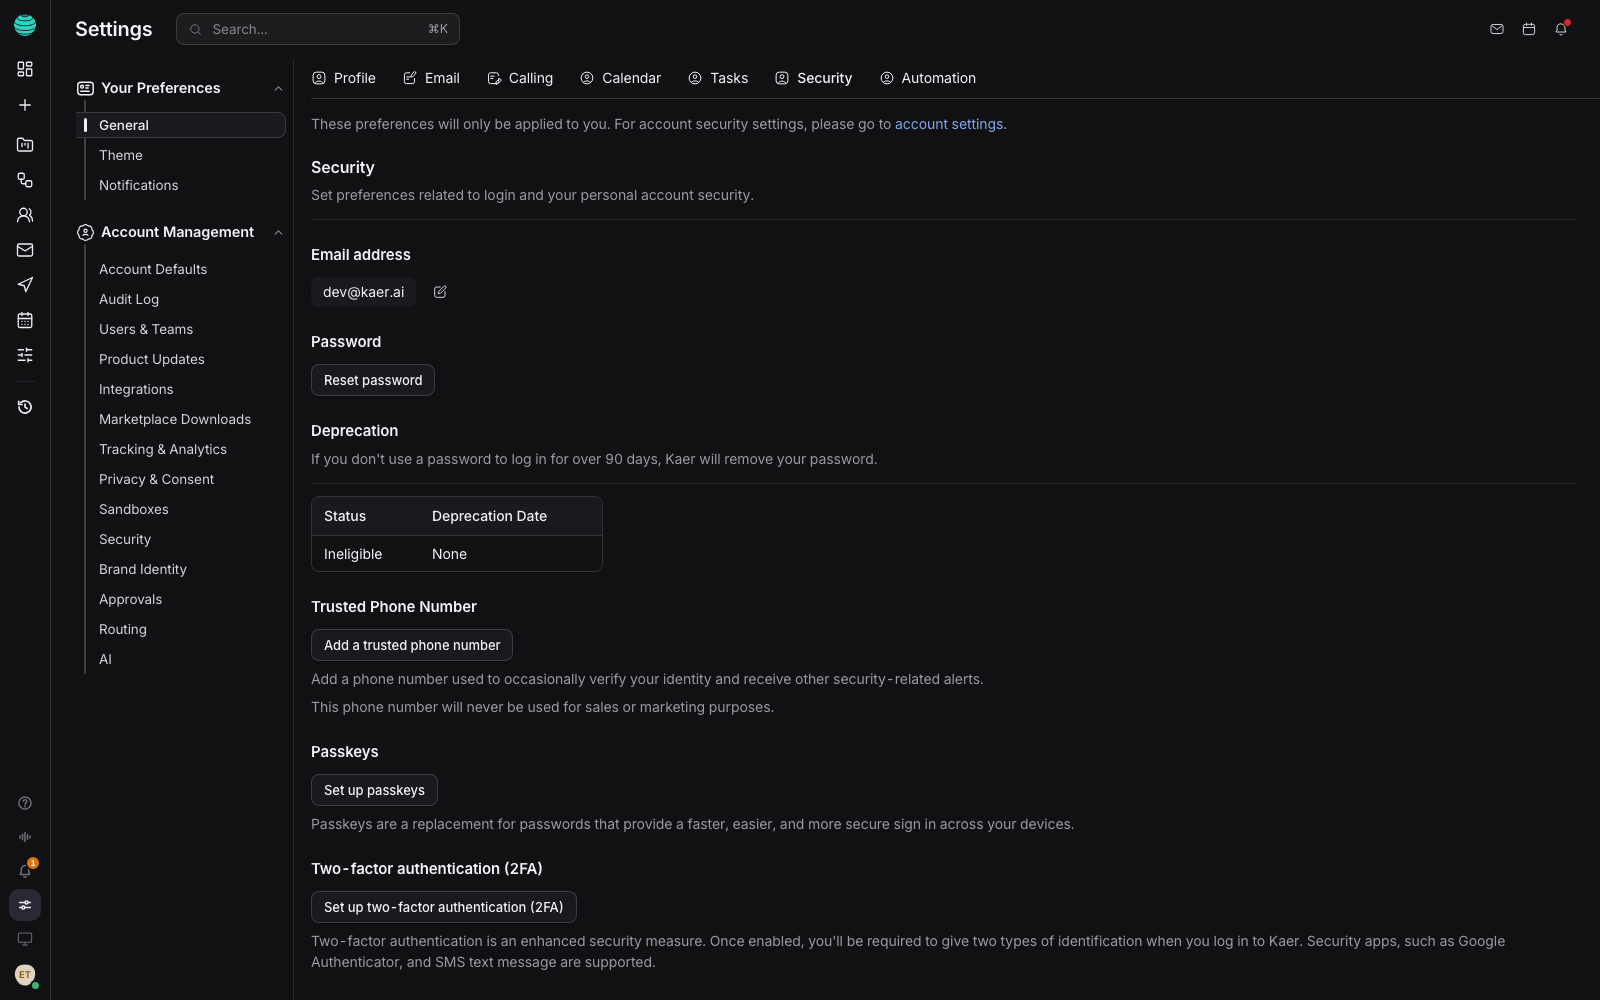
Kaer never requests admin. Each integration token carries exactly the scopes the task needs — granted automatically for low-risk reads, gated behind a one-tap approval for anything that writes to production. Revoke any single scope without touching the others.
The checks, the chasing and the month-end reconciliation that stay on a list until something breaks. Each one runs on a schedule with a scoped, revocable token, and stops at the step that would cost you something if it were wrong.
Every action outside your approved scope pauses and waits for a one-tap sign-off. Kaer never escalates its own permissions.
Tokens ship with the narrowest scope that completes the task. Deploy staging never implies deploy production — ever.
Every action, approval and scope grant is timestamped and attributable. Export it as CSV. Query it from your SIEM.
Kaer runs the whole runbook end-to-end — until it hits a gate. It pauses at the exact step that needs a human decision, explains what it needs, and resumes the rest automatically the moment you approve.
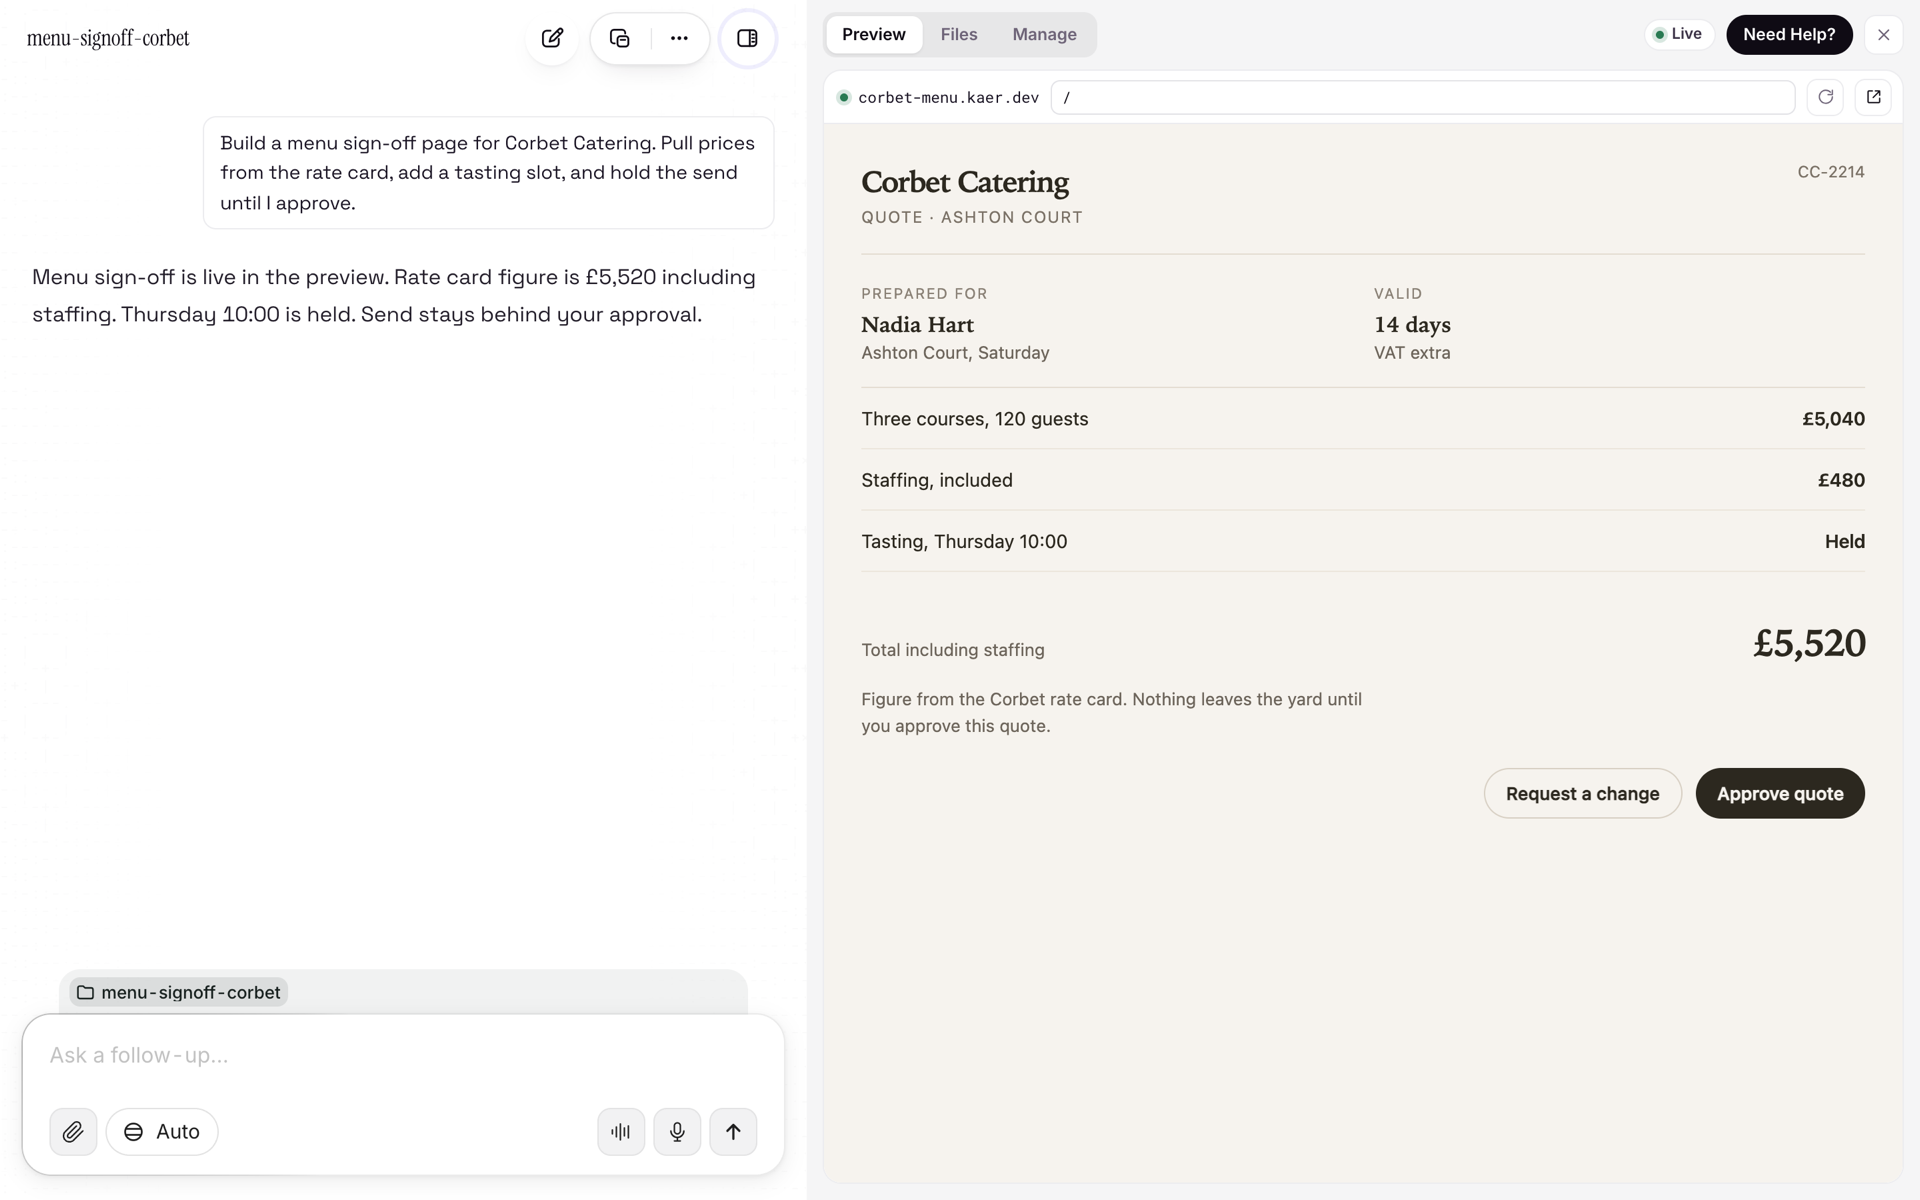
Every step Kaer takes — and every approval your team grants — is timestamped, named, and written to the audit log.
Every agent action carries the scope it used; every human approval records who signed off, when, and exactly what they permitted. Export it as CSV, push it to your SIEM, or query it directly. The trail is yours.
Kaer runs the repetitive parts of your runbooks automatically, pauses for every decision that matters, and leaves a full trail your team and your auditors can read. Safe by default — not by accident.